Some links carry values that matter: an affiliate id, an order number, a date. Anyone can edit a link before clicking it, so the page it opens cannot trust those values on their own.
A signed link adds a fingerprint of the values, made with a secret only you and your website know. Your page rebuilds the fingerprint and compares; if anyone changed a value, the two do not match.
Where to find it:
The hash markers work in any email: broadcasts, automation emails and templates. The secret is in Setup, then Settings, under 🔐 Signing secret.
How a hash block works:
Put {{#sha256}} before the text and {{/sha256}} after it. When the email goes out, everything between the markers is worked out first (merge codes, custom fields, tag codes and snippets all fill in as usual) and the finished text is replaced by its SHA-256 hash: 64 characters of letters and numbers.
{{#sha256}}{{email}}|{{custom.affiliate_id}}|{{today}}{{/sha256}}
Spaces and line breaks around the text inside the block are ignored, so tidy formatting in the editor does not change the hash.
Adding a secret:
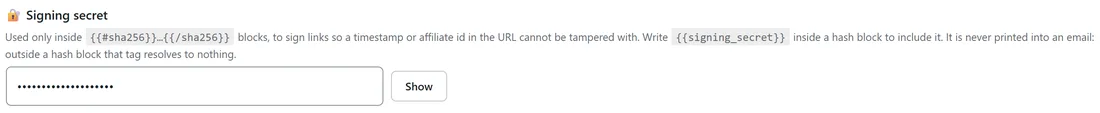
Without a secret, anyone who knows your recipe could build a matching hash. Add a secret only you know:
- Open Setup, then Settings, and scroll to 🔐 Signing secret.
- Type a long random secret into the box. Show lets you check what you typed.
- Press Save Settings.
- Write {{signing_secret}} inside the hash block, wherever your website expects it.
{{#sha256}}{{custom.order_id}}{{signing_secret}}{{/sha256}}
The secret is only ever readable inside a hash block. Anywhere else in an email {{signing_secret}} prints nothing at all, so it can never end up in a message by accident.
Building a signed link:
A signed link usually carries the values in plain sight and the hash beside them:
https://yoursite.com/partner/?id={{custom.affiliate_id}}&sig={{#sha256}}{{custom.affiliate_id}}{{signing_secret}}{{/sha256}}
- Write the link in the Code view of the editor, so the editor keeps every character exactly as typed.
- Use the same values, in the same order, inside the hash block as your page will use.
- Send yourself a test, or check the preview, and look at the link: the sig value should be 64 characters.
Checking it on your website:
Your page, script or membership plugin does the same sum: it takes the values from the link, joins them in the same order with the same secret, makes the SHA-256 hash, and compares it with sig. If they match, the values are exactly what you sent. If not, the link was changed, and the page can refuse it.
A real example:
Leafwise Gardening pays partners for seed referrals. Each partner has an affiliate_id custom field. Anna sets a long signing secret in Settings, and the partner email links to:
https://yoursite.com/partner/?id={{custom.affiliate_id}}&sig={{#sha256}}{{custom.affiliate_id}}{{signing_secret}}{{/sha256}}
Her partner page joins the id with the same secret, hashes it and compares. When a partner edits the id to someone else's, the sig no longer matches and the page shows a friendly "please use the link from your email" message instead of crediting the wrong person.
Tips:
- Use a long random secret, at least 32 characters, and keep it out of your emails and screenshots.
- Put a date such as {{today}} in the block when a link should only work for a while; your page then checks the date too.
- Keep the order of values written down next to your page's code, so both sides always match.
- If you change the secret, links in emails already sent no longer match, so change it between campaigns.